How to Fix the Insufficient Privileges Error in Salesforce (Admin & User Guide)

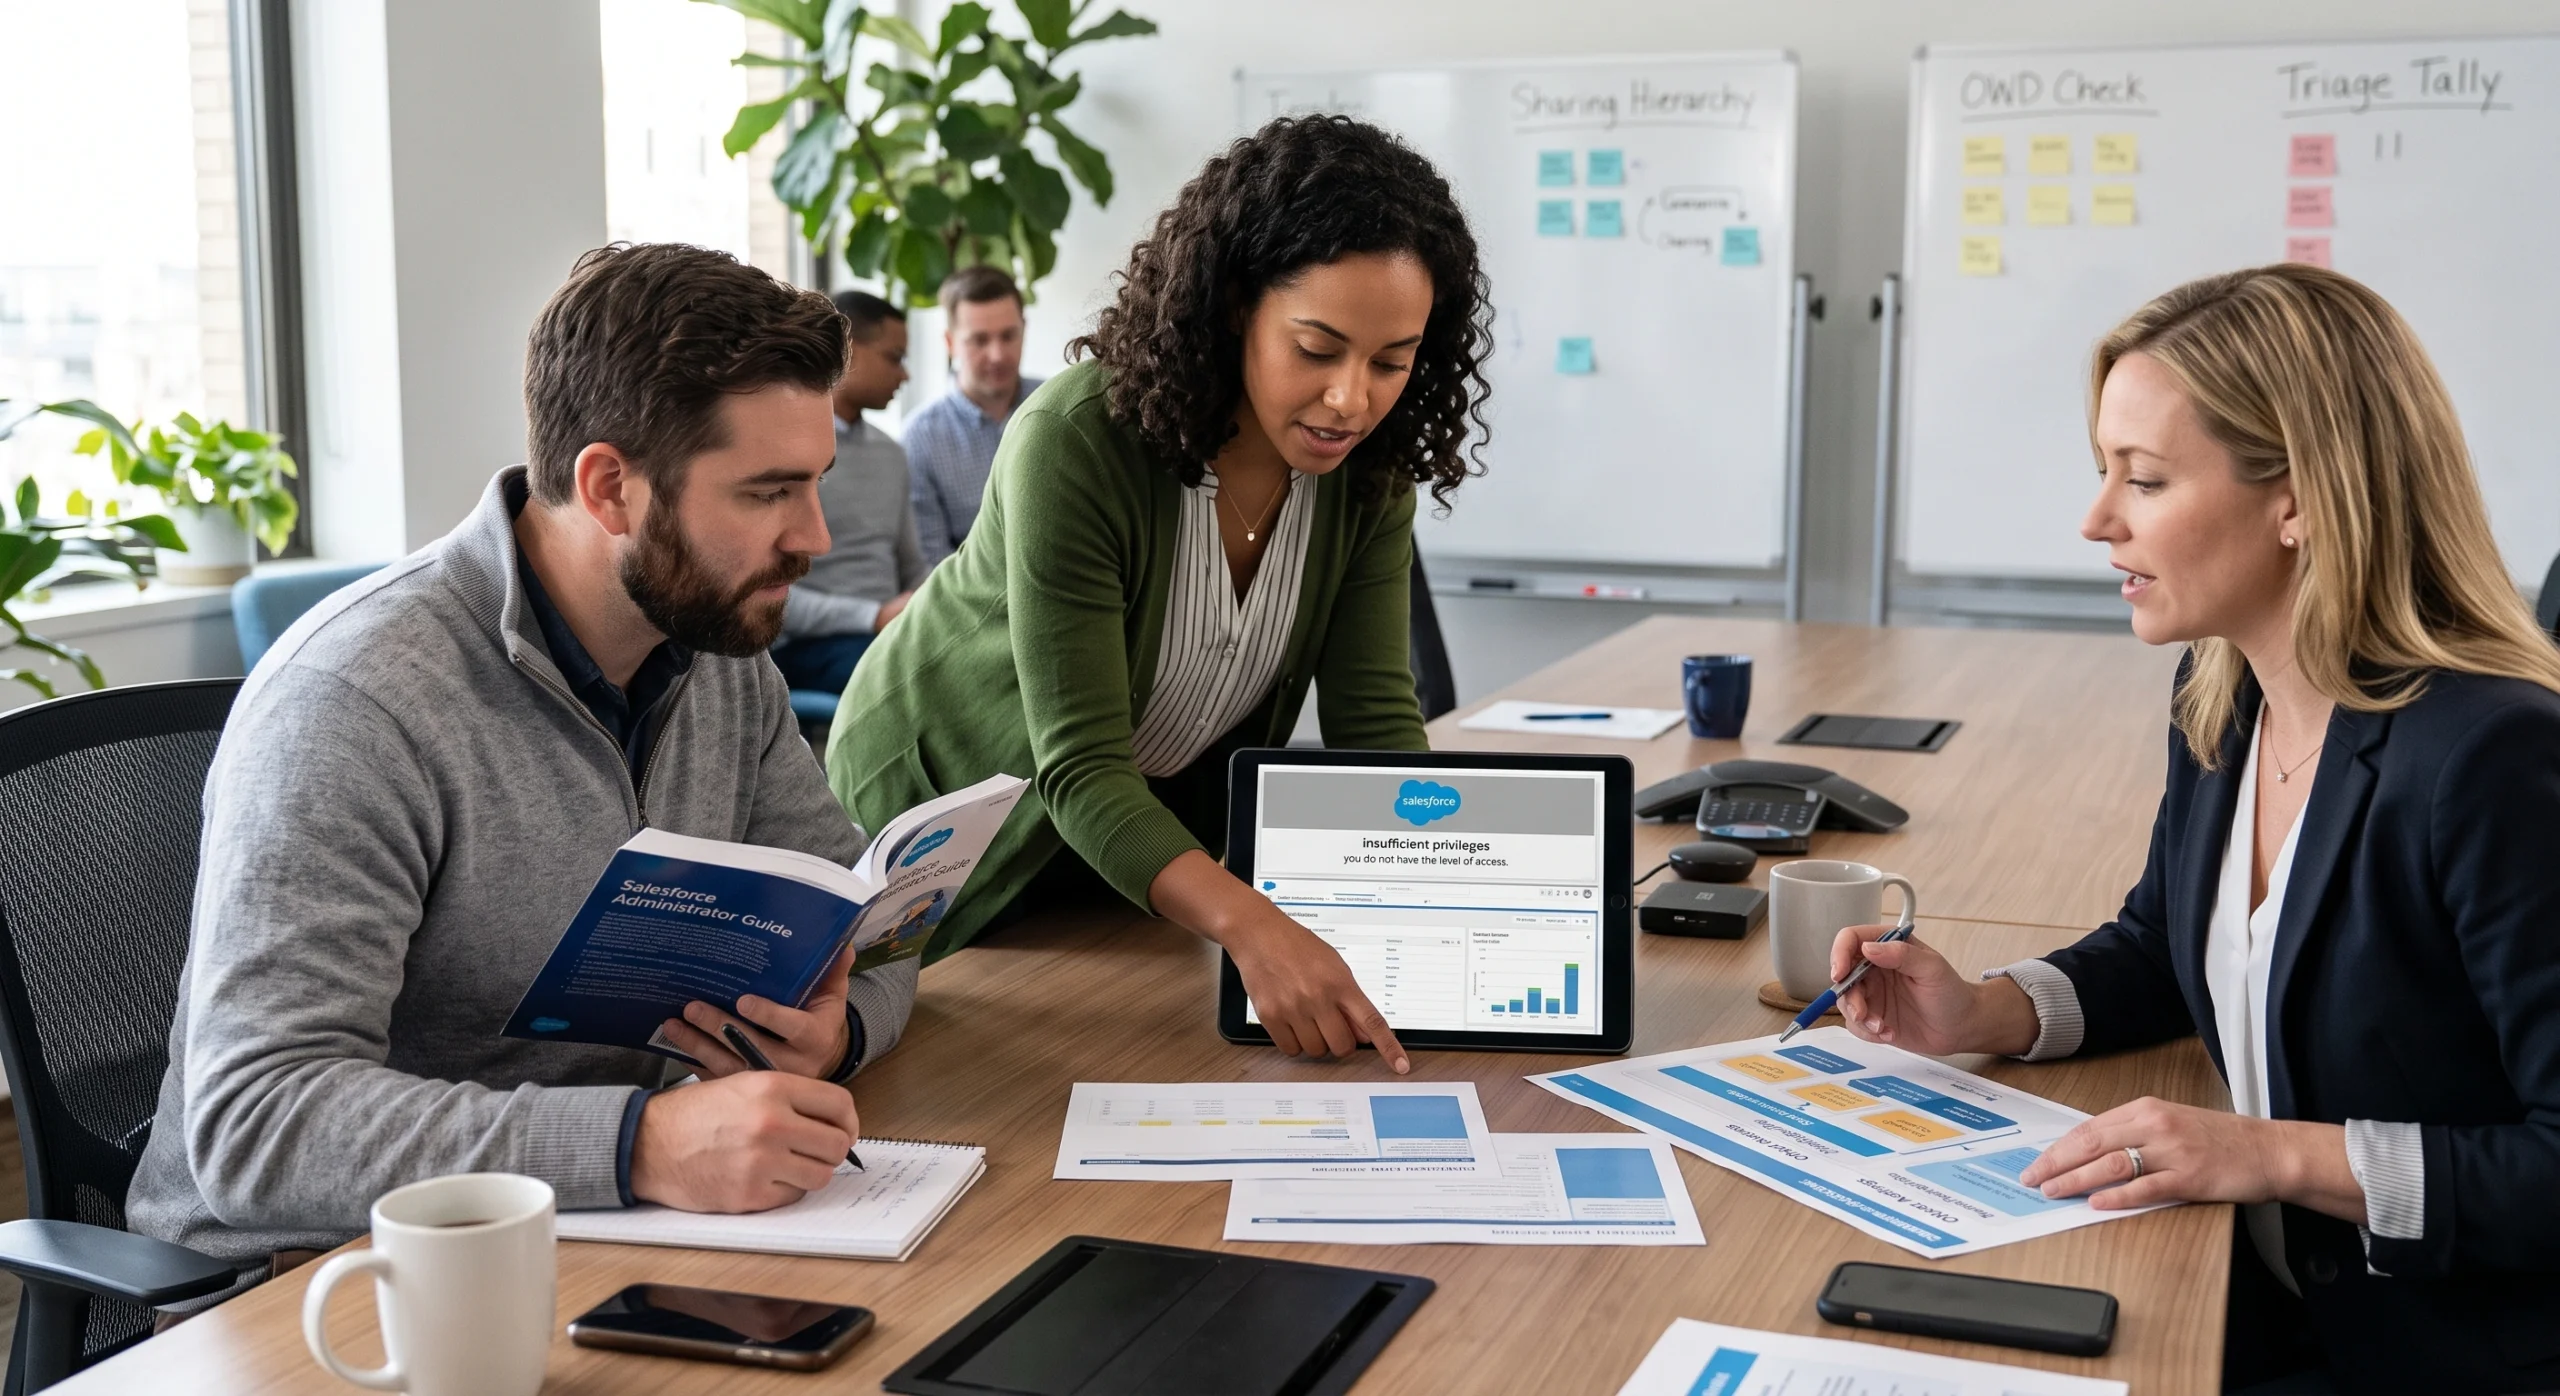
Picture this: your top sales rep is two minutes away from an urgent client pitch, tries opening a major pipeline deal, and runs smack into a plain gray roadblock. No records, no contact numbers, just that irritating system banner staring back at them: salesforce error insufficient privileges you do not have the level of access.
Few things trigger panic across a revenue team faster than unexpected salesforce insufficient privileges. Reps immediately jump into Slack to report the platform is broken, tickets flood your queue, and forward momentum grinds to a total halt.
The reality? Running into insufficient privileges in salesforce almost never means the software crashed. It actually means Salesforce is doing what it was engineered to do from day one: lock down sensitive company data. Think of it as a corporate bank vault. If a user’s assigned profile, hierarchy level, or manual sharing rules lack the exact keycard for that specific door, the platform slams it shut on purpose.
Sorting out salesforce insufficient privileges should not demand hours of blind guesswork across your backend setup. Once you understand why the block pops up, tracing the problem through your security settings gets straightforward. In this hands-on guide, we will step through every barrier, from foundational sharing configurations down to tricky cross-object lookups, so you can learn how to fix insufficient privileges error in salesforce quickly and get your staff back to real work.
Table of Contents
ToggleUnderstanding the Architecture: Why Do Users Get Insufficient Privileges in Salesforce?
When an employee submits an urgent support ticket, their first reaction is almost always confusion: why do i get insufficient privileges in salesforce? Most assume their browser cache glitched or an IT technician accidentally deactivated their login. Behind the scenes, however, Salesforce’s security gatekeeper evaluates every interaction against a strict hierarchy before serving up any database record.
The platform relies on an onion-style security model rather than a simple on-off switch. The moment someone clicks an opportunity or lead, the engine verifies object permissions, inspects specific field-level boundaries, and scans record ownership rules. If even one gate remains locked, the screen displays a salesforce insufficient privileges message. This design mirrors the core principles outlined in the OWASP Access Control Cheat Sheet, ensuring sensitive business data remains protected through strict default-deny policies.
This is where balancing the salesforce permission set vs profile access becomes critical for administrators. While a profile establishes a user’s baseline floor, permission sets grant modular access without forcing admins to rebuild complex profiles. If a profile blocks access entirely, sharing rules cannot override that boundary, leaving the user stuck with salesforce insufficient privileges until the profile mismatch is corrected.
When teams fail to resolve these access roadblocks quickly, revenue pipelines stall and reps lose productive selling hours. Many modern enterprises solve these recurring administrative logjams by taking notes from a practical framework to streamline daily business operations, ensuring internal permission workflows move fast without creating data blind spots.
Step-by-Step Resolution: How to Fix Insufficient Privileges Error in Salesforce
Troubleshooting salesforce insufficient privileges does not require tearing apart your entire production setup. When an employee flags a permissions deadlock, following a systematic, step-by-step diagnostic workflow gets records back in front of the right eyes in minutes rather than hours. Here is the field-tested method for how to fix insufficient privileges error in salesforce.
Step 1: CRED Check ──► Step 2: OWD & Hierarchy ──► Step 3: Sharing Rules ──► Step 4: Sharing Hierarchy ──► Step 5: Related Objects
Step 1: Inspect Object and Field Permissions
Start with the absolute basics before digging into complex visibility rules. Navigate to Setup > Users > Profiles (or check assigned Permission Sets) and verify the baseline CRED (Create, Read, Edit, Delete) permissions on the target object. If the rep needs to update pipeline records but their assigned profile only has “Read” rights enabled, the system drops an instant salesforce insufficient privileges block. Additionally, review field level security salesforce fls settings across all required fields. If an automation fires during save and tries to update a restricted field, the operation fails immediately.
Step 2: Check Organization-Wide Defaults (OWD) and Hierarchy
If object-level permissions look solid, move to Setup > Security > Sharing Settings. Review the baseline rules under salesforce organization wide defaults owd. If the object is set to “Private” or “Public Read-Only,” users cannot touch records they do not personally own without explicit sharing grants, and salesforce insufficient privileges is what they will see. For custom objects, always verify whether the “Grant Access Using Hierarchies” setting is toggled on; if disabled, managers sitting higher in the branch will remain completely blind to subordinate records.
Step 3: Review Sharing Rules and Criteria
When default settings are locked down tight, look at your exception architecture. Inspect salesforce sharing rules and role hierarchy settings to confirm whether ownership-based or criteria-based sharing rules cover the affected user. If a sales rep transfers to a new regional territory or switches public groups, existing sharing rules might fail to match their new role attributes, triggering salesforce insufficient privileges upon record access. In this scenario, update the user’s group assignments so the rules match again.
Step 4: Use the “Sharing Hierarchy” Diagnostic Button
Stop guessing why someone gets salesforce insufficient privileges on a lead or account. Jump directly onto the problem record, locate the action menu, and select Sharing Hierarchy. This native feature is the simplest answer to how to check record access in salesforce admin. It lists every team member, displays their effective permission level (Read, Read/Write, or Full Access), and explicitly spells out why access was granted or withheld, whether through manual sharing, a group rule, or role inheritance.
Step 5: Verify Lookup and Master-Detail Dependencies
If the user holds clear rights to the primary record but still hits a wall during save, inspect all related lookup and master-detail relationships. This is where salesforce insufficient privileges on cross reference entity sneaks in. In master-detail setups, child record access is strictly governed by the parent record’s security settings. If a user tries saving an invoice item linked to an account they cannot view, Salesforce blocks the entire transaction. Resolving permissions on the lookup target clears salesforce insufficient privileges without altering primary object security.
For diagnosing complex root causes and permission-blocking scenarios, cross-reference the official Salesforce Insufficient Privileges Troubleshooting Guide to ensure adjustments follow recommended administrative procedures without compromising data security.
Troubleshooting Edge Cases: Apex, Automation, and Layouts
Sometimes, an admin checks every standard permission, confirms everything is green, and the user still runs into an immediate brick wall. These tricky salesforce insufficient privileges cases happen when interface elements or background code silently clash with user permissions.
The first common culprit pops up inside Lightning App Builder and dynamic page layouts. If a page uses conditional component visibility, or if a custom Lightning component relies on an Apex controller that queries restricted metadata, users hit salesforce insufficient privileges the moment the record finishes loading. The issue is not the page itself; the underlying Lightning canvas is simply trying to pull values from data tables the user has zero permission to view.
The second major trigger involves automated background processes. When an account executive edits an opportunity, a record-triggered Flow or validation rule might fire behind the scenes. If that Flow runs in “User Context” rather than “System Context” and attempts to create an audit log or update a related child record the rep cannot edit, the entire save operation fails. The platform rolls back the update and throws the classic salesforce insufficient privileges banner. Resolving these process bottlenecks requires designing background triggers that respect data boundaries without breaking everyday workflows. You can reference this practical business process automation guide to structure automated workflows cleanly so background jobs run without locking frontline users out of core tasks.
Finally, watch out for integration settings like the “API Only User” permission. If an administrator accidentally assigns an integration profile or permission set with this box checked to a real employee, that user can run API queries through tools like Postman, but the moment they log in via a browser, the platform halts the session with salesforce insufficient privileges. Keeping dedicated service accounts isolated from standard user licenses prevents these accidental lockouts before they disrupt the workday.
How End Users Should Report Access Errors to Admins
When a permissions block halts urgent work, sending a vague Slack message like “Salesforce is broken” forces your system administrator into a frustrating guessing game. To clear salesforce insufficient privileges quickly, end users should provide actionable diagnostic details right out of the gate.
Supplying these three critical data points cuts triage time in half for any salesforce insufficient privileges ticket:
- The Exact Record URL: Copy and paste the full browser link directly from the address bar so the admin can instantly locate the record and pull up its sharing hierarchy.
- A Full Screen Capture with Timestamp: Share a complete screenshot that captures the salesforce insufficient privileges banner, along with your current time zone.
- The Specific Action Attempted: Clarify whether you were merely viewing the file, adjusting an opportunity stage, editing a custom field, or attempting to reassign ownership.
Following this simple reporting habit helps admins diagnose whether the roadblock stems from sharing rules or hidden field barriers in minutes.
Admin Best Practices: Preventing Access Roadblocks at Scale
Fixing user permissions after a team-wide crisis wastes valuable development cycles. Smart systems teams establish scalable administrative guardrails to stop salesforce insufficient privileges before it ever surfaces in front of end users.
- Adopt Modular Permission Set Groups: Stop cloning bloated user profiles every time a department shifts responsibilities. Build lean baseline profiles and use Permission Set Groups to grant granular capabilities cleanly.
- Audit Sharing Architecture Before Reorgs: Prior to realigning sales territories or merging operational branches, conduct a comprehensive audit of your sharing rules and role hierarchy. Verify that automated assignments reflect new management paths so reps do not hit sudden access roadblocks.
- Rigorous Sandbox Validation with “Log In As”: Never deploy new validation rules, record types, or automated flows straight to production. Test new setups in an isolated Sandbox environment and use the “Log In As” feature under target user credentials to confirm they complete everyday edits without hitting salesforce insufficient privileges.
Frequently Asked Questions About Salesforce Access Errors
Q1: Why do I get insufficient privileges in Salesforce when I am the record owner?
Even if you own the record, salesforce insufficient privileges typically happens when the record enters a locked approval process, switches to a read-only record type, or triggers a validation rule requiring fields restricted by field level security.
Q2: What is the difference between sharing rules and role hierarchy?
A role hierarchy controls vertical data access, naturally opening subordinate records to managers sitting above them. Sharing rules work horizontally to create lateral exceptions, such as granting cross-departmental visibility between marketing and regional sales teams who share the same tier.
Q3: How does Salesforce evaluate record access behind the scenes?
Salesforce enforces access through an orderly five-step evaluation funnel:
- Object CRED Permissions: Checks if the user’s profile or permission sets permit the base action.
- Organization-Wide Defaults (OWD): Verifies the company baseline security floor (Private vs. Public).
- Role Hierarchy: Grants access upward to higher branches if hierarchy sharing is toggled on.
- Sharing Rules: Evaluates criteria-based and ownership-based lateral access grants.
- Manual Sharing & Teams: Grants final visibility through explicit user-to-user record sharing.
Understanding this chain shows admins exactly where to look, so the salesforce error insufficient privileges you do not have the level of access can be resolved with precision.

About Adam
Adam is a blogger with over 10 years of experience writing about business growth, SaaS, digital marketing and finance. At OutreachHunt, he shares practical, research-backed guides for founders, marketers and working professionals.
View all posts by Adam